● EnvForge v1.0.3 · 28 AI safety tools · Rust · source-available · VS Code, IntelliJ, Neovim, Zed
Your secrets aren’t safe from AI.
An AI agent is a process with read access to your working directory and an outbound network connection. EnvForge is designed for that. Fence the files, intercept the tool calls, run with secrets sealed in memory, and trip a canary if anything leaks. One Rust CLI, a TUI, and a Language Server that lights up your editor.
Four moves.
EnvForge isn’t a vault you push to and forget. It’s a defense pipeline you run as you work — fence, guard, run, watch.
FENCE
Fence adds ignore files and rules so AI tools are less likely to read secret files, then hands them context without values — types and names from an inferred schema, never the credentials themselves. This is not a sandbox. Terminal and MCP can still bypass ignore files. See the integration matrix for covered vs fallback.
# write ignore/rules for configured AI tools
$ envforge fence
  created .envforgeignore · .cursorignore · .claude/settings.json

# give the agent context — names & types, no values
$ envforge schema emit-ai --infer --output .env.ai.md
  wrote .env.ai.md (42 variables, 0 values)
GUARD
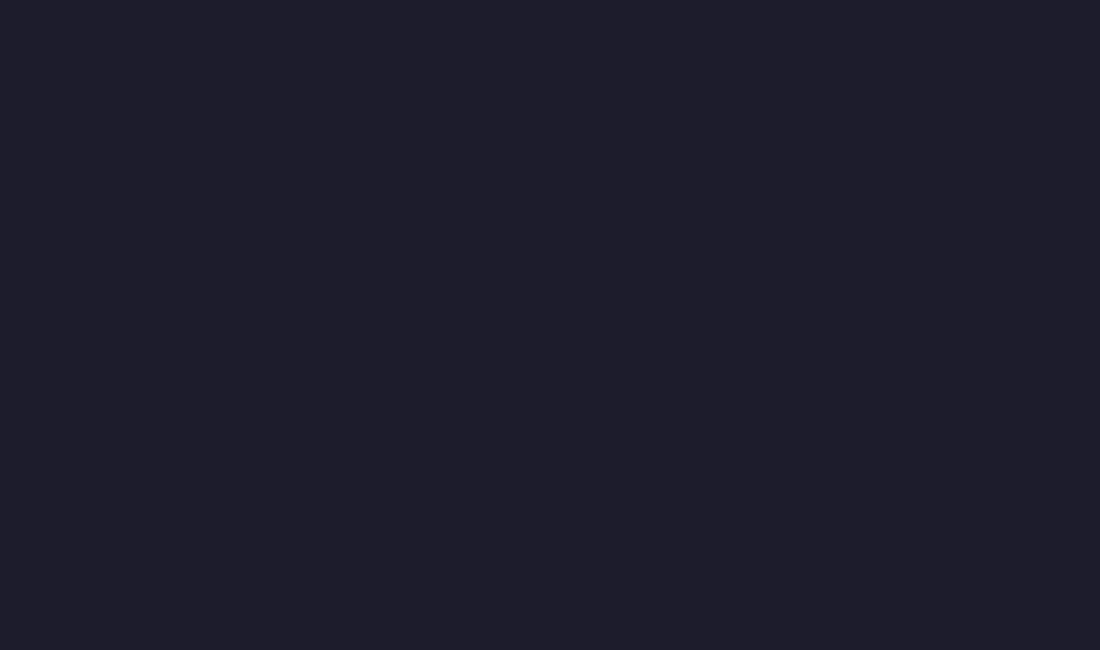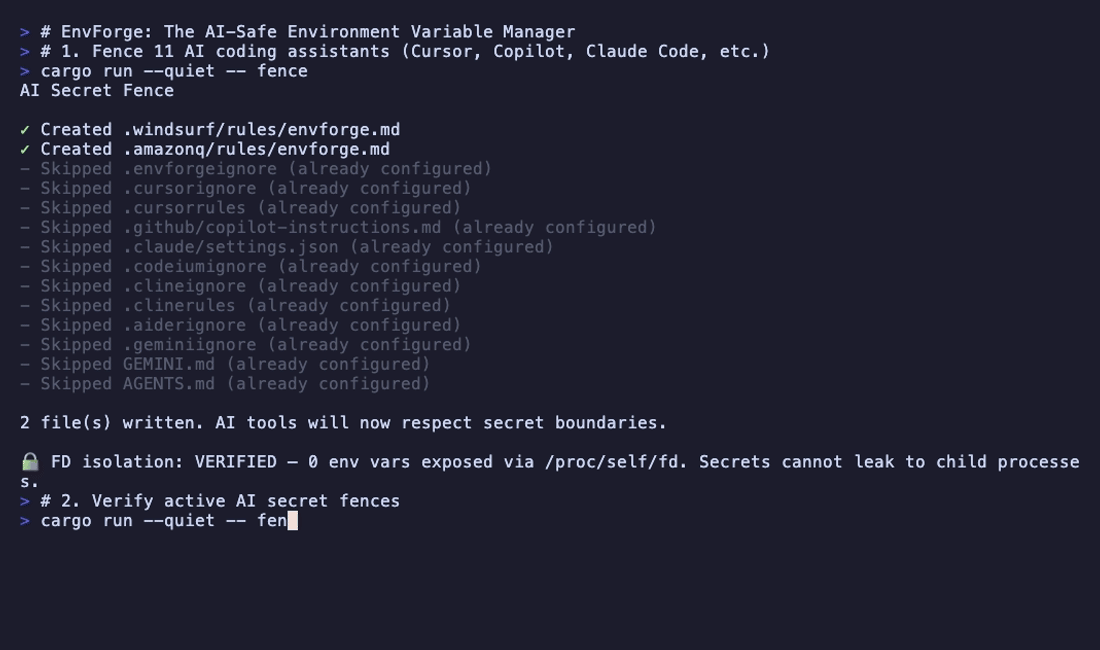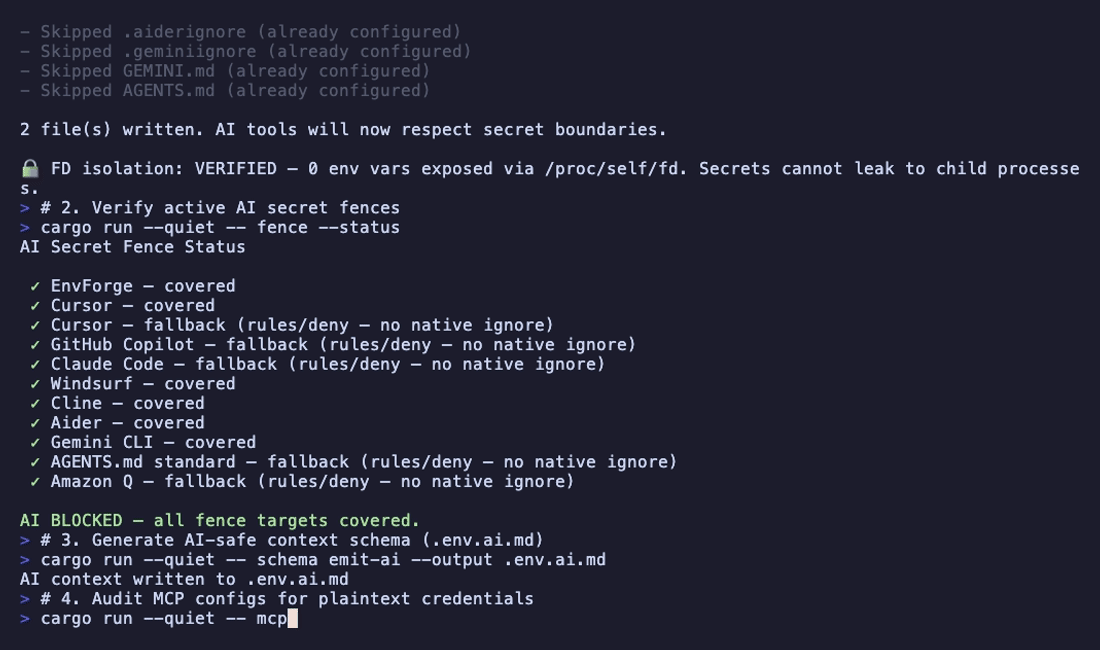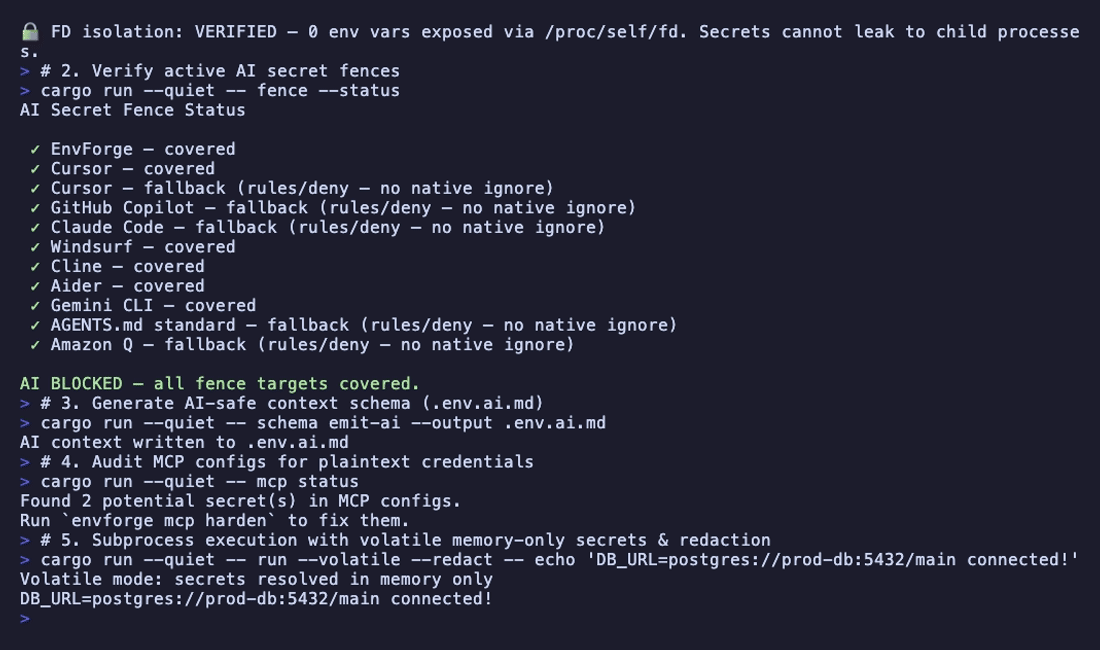
Wire EnvForge into the agent’s tool loop and your git hooks. Every read and every commit is scanned before it lands; leaked credentials in MCP configs get rewritten to ${VAR} references.
# PreToolUse + PostToolUse hooks in the agent
$ envforge ai-hook install claude-code
  hooks installed: PreToolUse + PostToolUse

$ envforge scan --install-hook
  pre-commit hook installed

$ envforge mcp harden
  2 credentials found → replaced with ${VAR}
RUN
Execute your app with secrets resolved in memory only and masked in every log line. Scope access to a time-boxed lease — and revoke everything instantly if something feels wrong.
# volatile = never on disk · redact = masked output
$ envforge run --volatile --redact -- npm start
  connecting to [REDACTED:DB_PASSWORD]@host…
  server running on :3000

$ envforge lease create --ttl 1h --keys DB_URL,API_KEY
$ envforge revoke --all
  KILLSWITCH: 3 leases revoked
WATCH
Plant honeypot canaries that alert when the fake value is seen in scanned tool output, logs, or files, audit git history for AI-assisted leaks, and map what breaks before you rotate. Detection and governance, not just prevention.
# honeypot credential — tripwire when the fake value is read or used
$ envforge canary create STRIPE_KEY
  canary planted · monitoring enabled

$ envforge audit --ai-leaks
  scanned 1,204 commits · 0 AI-assisted leaks

$ envforge deps DB_URL
  3 services depend on this secret
See the danger in your editor.
EnvForge ships a Language Server and first-party VS Code, IntelliJ, Neovim & Zed plugins. The AI-exposure story lives where you write code — not buried in a CLI. Zed has no gutter or status bar yet.
- Exposure heatmap — a colored dot in the gutter on every env-var line. It shows exactly the same result as the command line. (VS Code, IntelliJ, Neovim — not Zed.)
- Canary tripwire glyphs — a shield replaces the dot when a canary is registered. Hover for status.
- Status-bar trio — variable count, fence shield (
AI BLOCKED/AI ALLOWED), and a live volatile-lease countdown. (Not on Zed.) - Env-file go-to-definition — jump from a key in
.envto its.env.schemasection. - MCP config linter — credential patterns flagged inline in
.cursor/mcp.json,.claude/settings.jsonand friends. - One-key quick-fixes — plant a canary, mark as secret, generate
.envfrom schema, swap in a secret reference.
REDplaintext, readable by AI agents right nowAMBERsensitive — will be redacted by AI-guardGREENfenced — ignore rules in place (not a sandbox)VS Code, IntelliJ, and Neovim share gutter and status-bar UI on the same envforge lsp engine. Marketplace plugins are versioned separately from the CLI (plugins 0.3.0, CLI 1.0.3). Zed is LSP only (no gutter or status bar). Also works through LSP alone in Helix, Emacs, Sublime Text, Kakoune & Lapce.
28 tools. Six layers.
From prevention to governance — fence, guard, run, and watch.
| Layer | Tool | Command | What it does |
|---|---|---|---|
| Prevention | Secret Fence | envforge fence | Ignore rules for Cursor, Copilot, Claude Code |
| Prevention | Fence Status | fence --status | Verify ignore rules are active |
| Prevention | Fence Targets | fence config | Choose which AI tools the fence covers |
| Prevention | Pre-Commit Hook | scan --install-hook | Block commits containing secrets |
| Prevention | 3-Stage AI Guard | ai-guard pre-tool | Scan before & after AI tool execution |
| Prevention | AI Hooks | ai-hook install | PreToolUse + PostToolUse hooks |
| Prevention | Hook Status | ai-hook status | Check which tools have active hooks |
| Prevention | File Alerts | built-in | Warn on .env, .pem, .ssh/ access |
| Runtime | Volatile Mode | run --volatile | Secrets in memory only — never on disk |
| Runtime | Log Redaction | run --redact | Mask secrets in subprocess output |
| Runtime | Credential Proxy | proxy --port 8100 | HTTP API with allowlist + audit |
| Runtime | Session Leases | lease create --ttl | Time-bounded secret access |
| Runtime | Killswitch | revoke --all | Instantly revoke all active leases |
| Context | AI-Safe Schema | schema emit-ai | Types & names without values |
| Context | Safe Export | export --safe | Redacted [REDACTED] values |
| Context | Ignore File | .envforgeignore | Mark files AI tools should skip |
| Remediation | MCP Scan | mcp status | Find creds in AI tool configs |
| Remediation | MCP Harden | mcp harden | Auto-replace with ${VAR} references |
| Remediation | Prompt Sanitizer | sanitize FILE | Strip secrets from any file |
| Detection | Canary Secrets | canary create | Honeypot credentials — alert when the fake value is seen in scanned output |
| Detection | AI Leak Audit | audit --ai-leaks | Scan git for AI-assisted leaks |
| Detection | Access Audit | audit --access | JSONL log of proxy access |
| Governance | Approval Flow | --require-approval | Human approves each secret access |
| Governance | Dependency Map | deps KEY --source | What breaks if this secret rotates? |
| Governance | External Scanner | scanner test | Multi-scanner pipeline (Lakera, ggshield) |
| Governance | Session Scoping | session start --ttl | Per-AI-tool scoping with auto-detection |
| Governance | Lifecycle Automation | lifecycle check | Rule-based create / rotate / decommission |
| Governance | Analytics | analytics unused | Dormant-secret detection & retention |
Beyond AI safety.
A complete environment-variable manager underneath — CLI + TUI, no migration required.
+Encrypted sync
Sync across machines through Git, with strong encryption (age). Pick which keys to sync, override values per machine, roll back, and work offline. Your env vars are stored encrypted in the repo — never in plain text.
+13 secret providers
Pull, push and reference across Vault, AWS SSM, 1Password, Doppler, GCP, Azure and more — with URI refs like vault://secret/app/DB_URL.
+Schema validation
.env.schema with types, defaults & descriptions. Drift detection, JSON Schema for autocomplete, onboarding wizard.
+TUI + CLI
Vim-style TUI with fuzzy search, grouping and masking. CLI commands with --json and --dry-run.
+8 export formats
dotenv, JSON, YAML, TOML, Docker, Docker Secrets, Kubernetes Secret, Terraform tfvars — one command.
+Workflows & audit
Profiles, snapshots, guided rotation with propagation, secure sharing, a unified check, plus envforge audit-trail report for a local audit report (useful for your own records). EnvForge is not SOC 2 certified.
Plugs into your stack.
Configure once, reference everywhere.
Install
Needs Rust 1.75+ (Homebrew tap builds from source), Linux or macOS.
# shell completions (auto-install)
$ envforge completions zsh --install

# IDE-style autocomplete: carapace / inshellisense / kiro / fig
$ envforge completions carapace --install

# built-in man pages
$ envforge man            # full command index
$ envforge man fence      # a specific command